Skip to content

Security Monitor

7 posts with the tag “Security Monitor”

End-of-Life Information for Applications
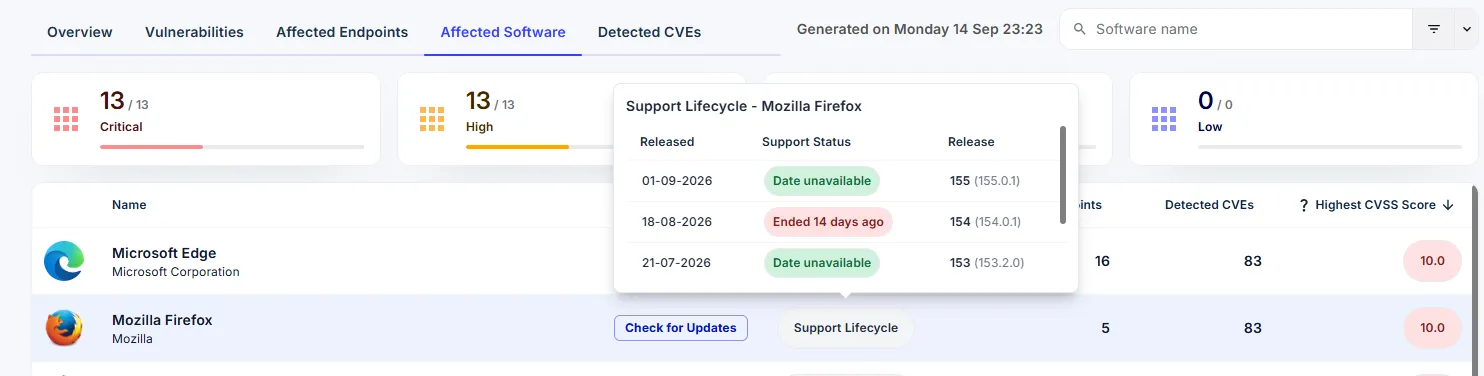
The Support Lifecycle panel for Mozilla Firefox, listing each version with its release date and support status, including one that ended 14 days ago

Software that has reached end of life stops receiving security updates. Every vulnerability found after that date stays open, and no patch is coming. Security Monitor now shows you where that applies in your own environment.

Open Affected Software and select Support Lifecycle on any application. You see each version installed on your endpoints, when it was released, and whether its support has ended.

For the security team, this answers three questions that used to mean checking vendor sites by hand:

  • Which applications in our environment are past their support date?
  • Is a fix still coming for this CVE, or is the version already end of life?
  • What do we put in front of an auditor about our exposure?

Working in deployment? Pass this on to your security colleagues. End-of-life dates are the kind of thing they track by hand today, and this puts the answer next to the vulnerability data they already use.
Local Administrators Widget

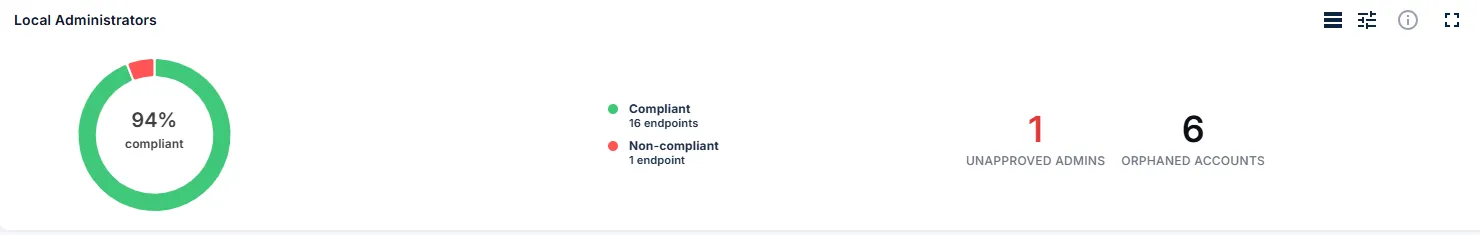
The Local Administrators widget showing 94% of endpoints compliant, one unapproved admin, and six orphaned accounts

Security Monitor now shows which local administrator accounts and groups exist on your endpoints — and which of them nobody approved.

You define the accounts and groups that belong there. Security Monitor checks every endpoint against that list and does the rest:

  • Unapproved admins — accounts or groups holding local administrator rights that are not on your list
  • Orphaned accounts — local accounts whose user no longer exists

The widget shows how many of your endpoints are compliant, so you can see the whole fleet at a glance and go straight to the ones that are not.

Blazing fast views

Blazing fast views

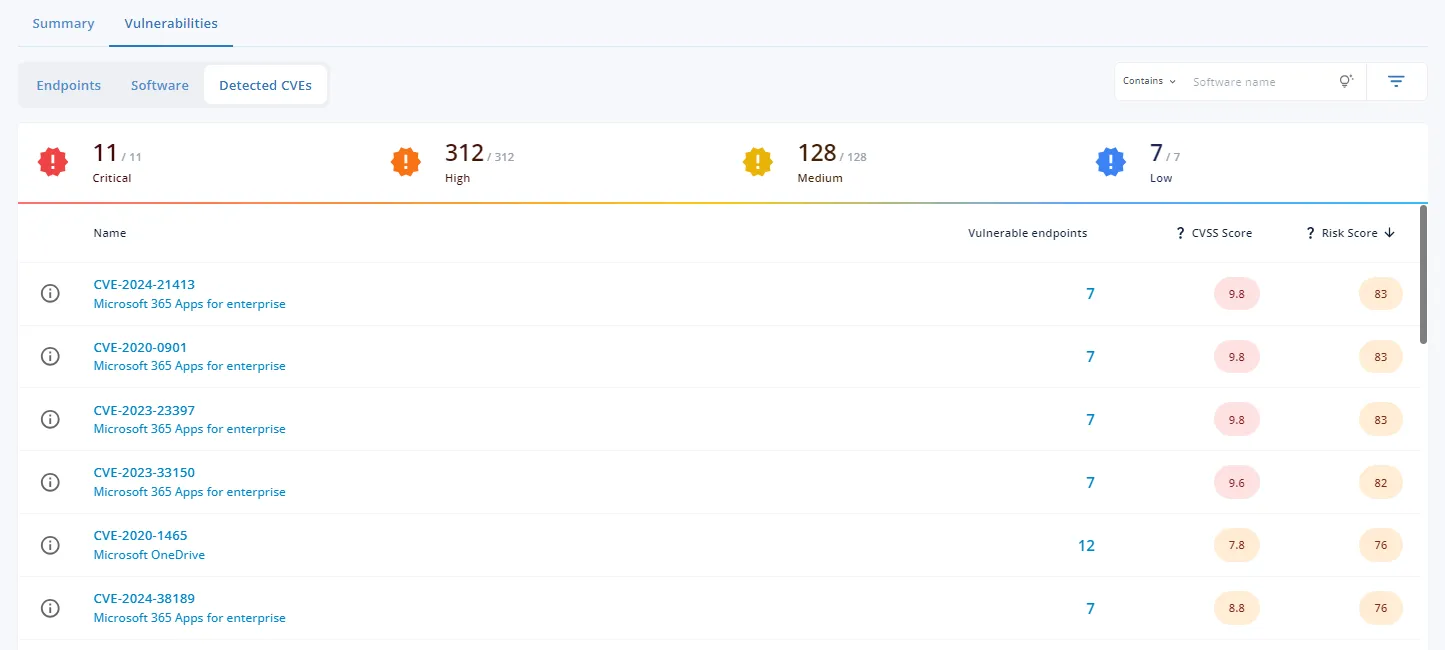
CapaOne Security now displays views over 92% faster. Previously customers with 5,000+ endpoints could see a 10-15 second delay before Endpoints, Software and Detected CVE views displayed; now under 1 second, even for 10,000+ endpoints.

Enhanced CVE matching

Enhanced CVE matching

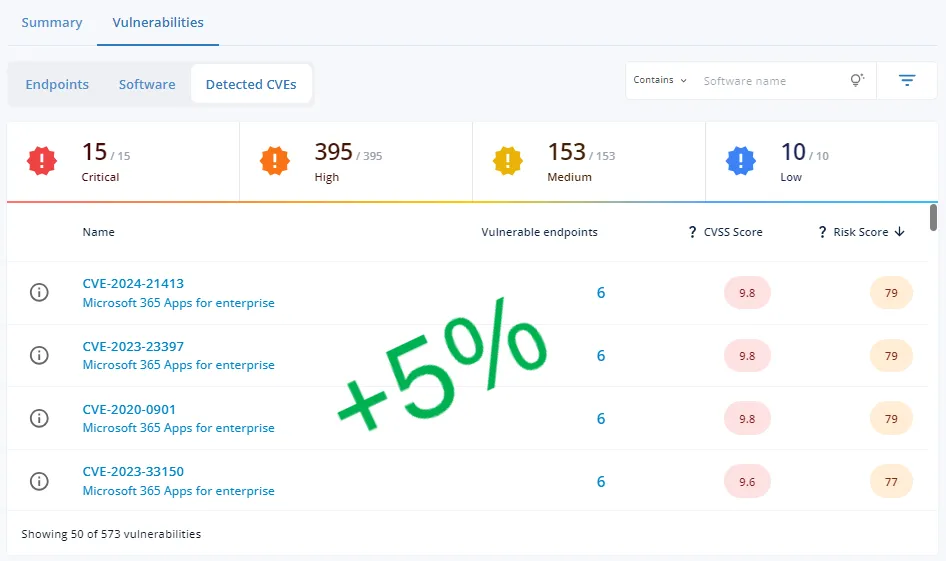
Enhanced CVE matching in CapaOne Security led to a 5% increase in vulnerability detection. Resolved issues with specific versions of 7-Zip and Adobe Acrobat that were not previously matched.

CapaOne Security

CapaOne Security

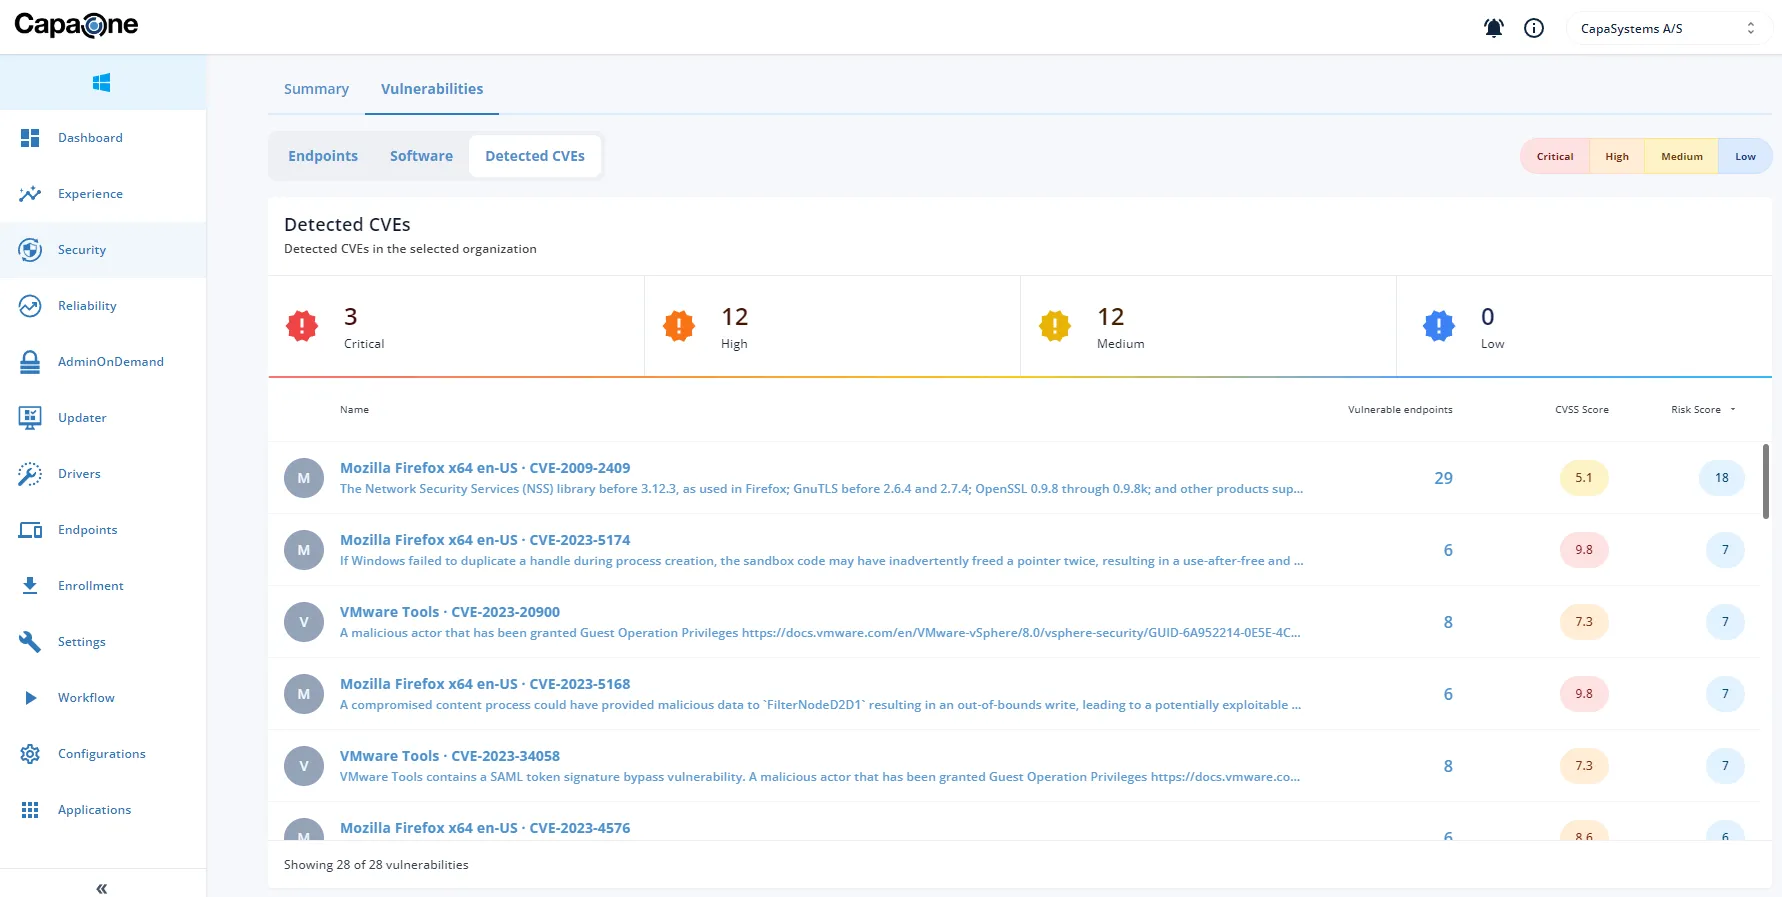
  • CVE detection — empowers staying ahead of cyberattacks.
  • NIS2 reporting — ensures an effortless compliance process.
  • CapaOne Security is moved to the main menu for quick and easy access.

CapaOne Security

CapaOne Security

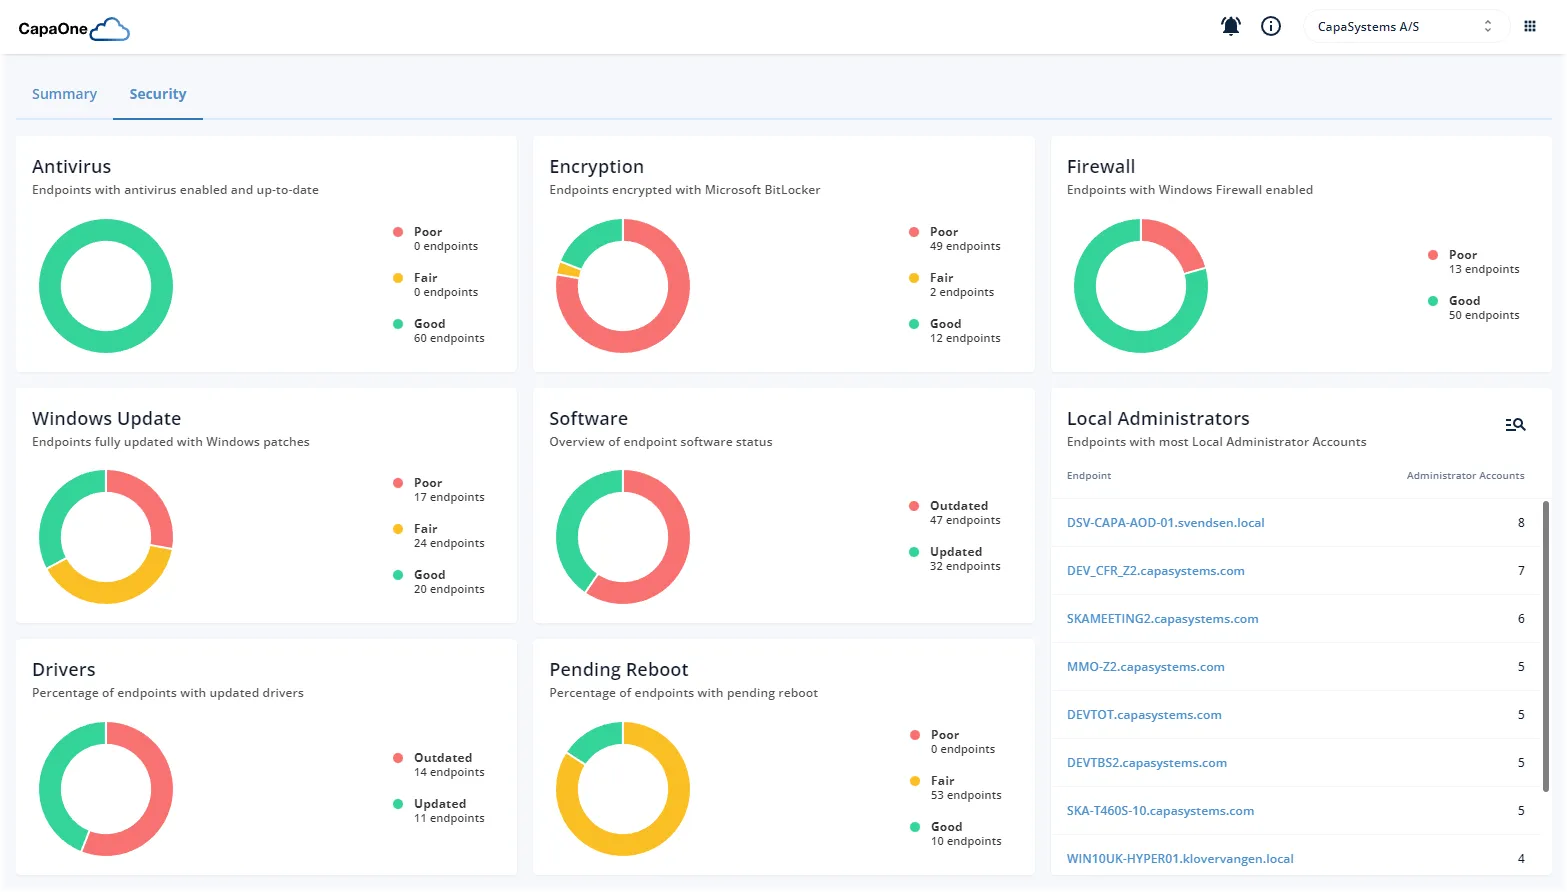
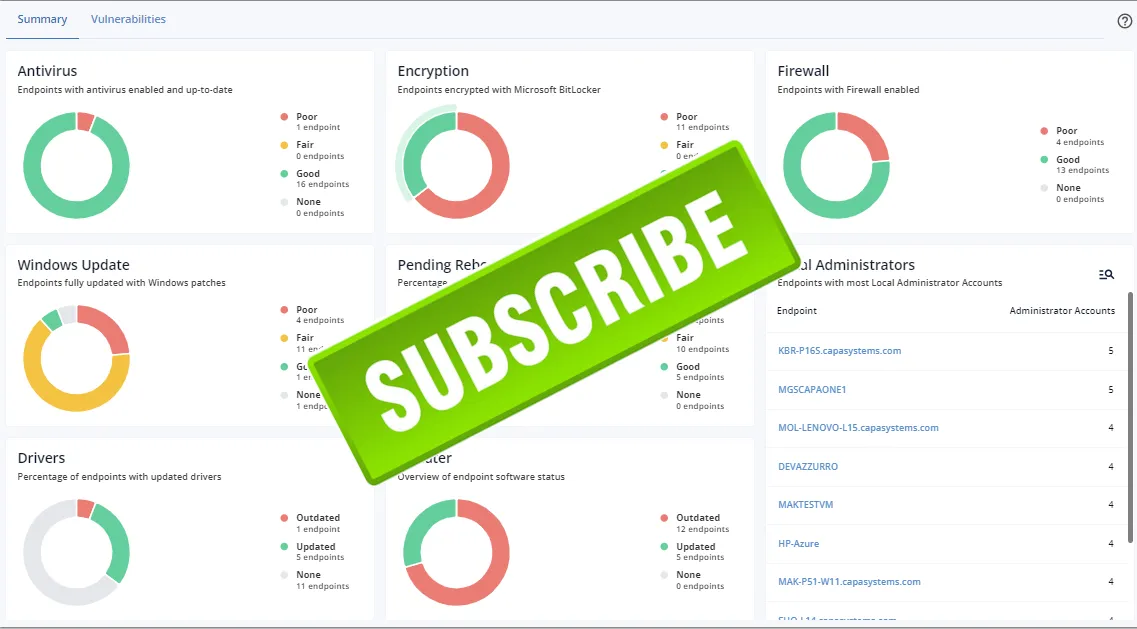
CapaOne Security monitors the most critical security configurations, hardware drivers, third-party software, and Windows patches — helps identify and pinpoint security vulnerabilities across all endpoints. Available now, free.