

CapaOne Security
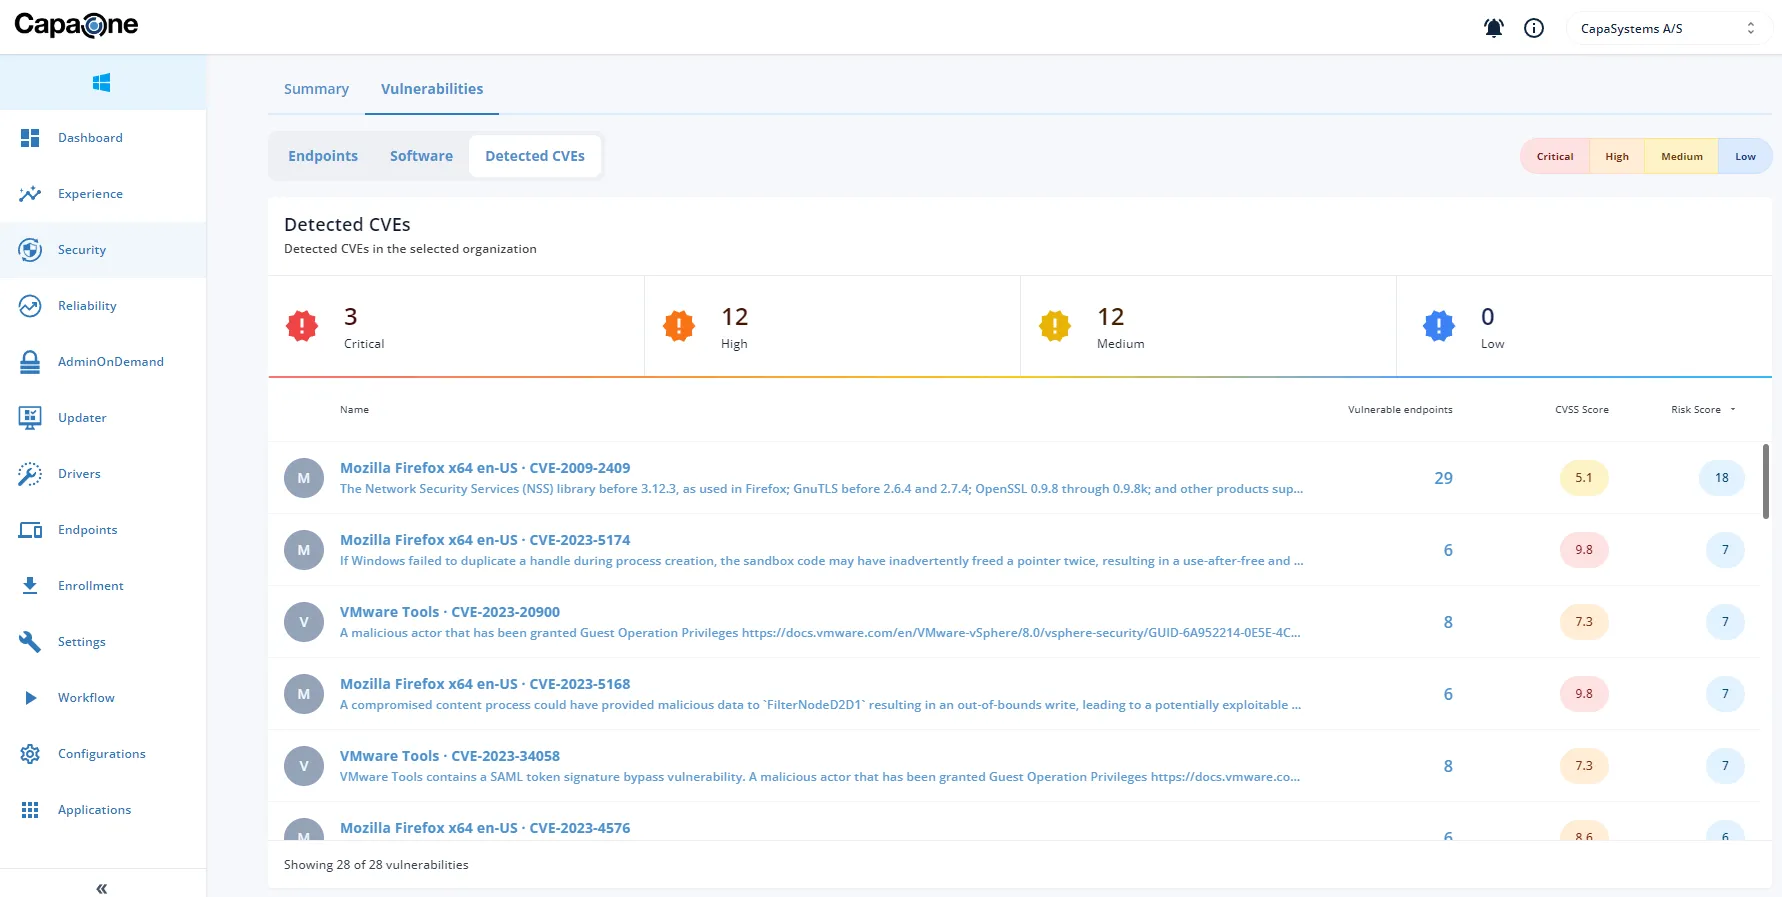
- CVE detection — empowers staying ahead of cyberattacks.
- NIS2 reporting — ensures an effortless compliance process.
- CapaOne Security is moved to the main menu for quick and easy access.
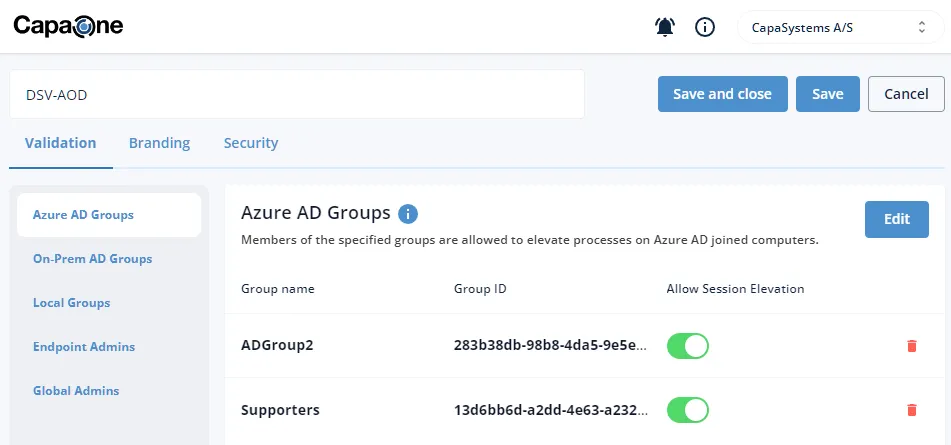
Azure AD groups (Entra ID groups) can now be used to validate users in CapaOne AdminOnDemand — makes it easy to specify users allowed to run elevated processes by selecting Azure AD groups from a drop-down list.
The CapaOne logo has been updated, reflecting a renewed commitment to efficient, scalable, and secure cloud solutions. Already live on websites; integrated into products over the following weeks.
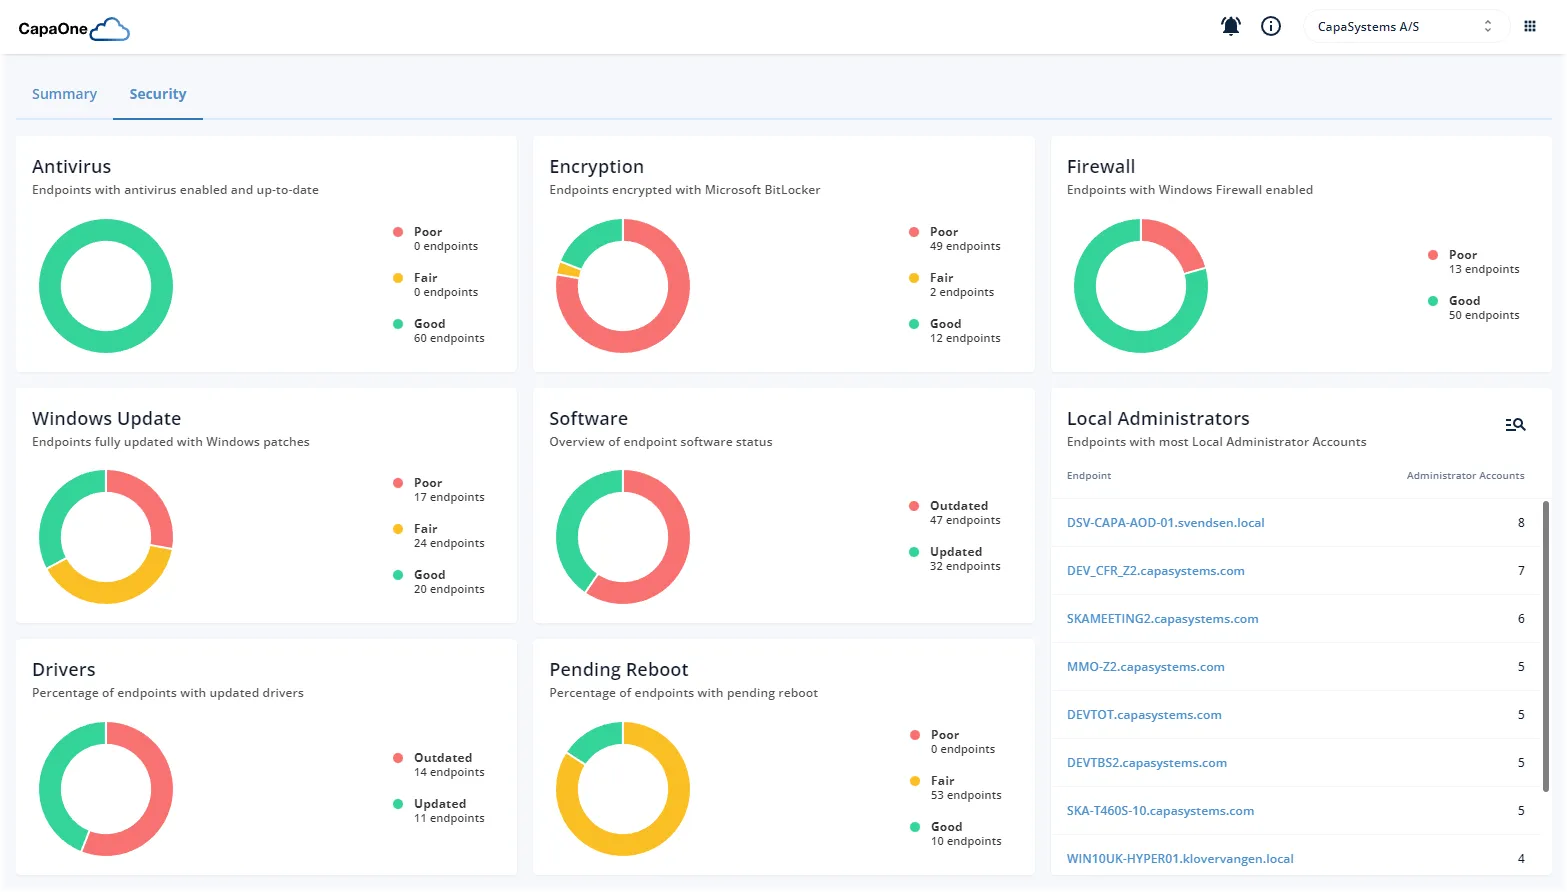
CapaOne Security monitors the most critical security configurations, hardware drivers, third-party software, and Windows patches — helps identify and pinpoint security vulnerabilities across all endpoints. Available now, free.
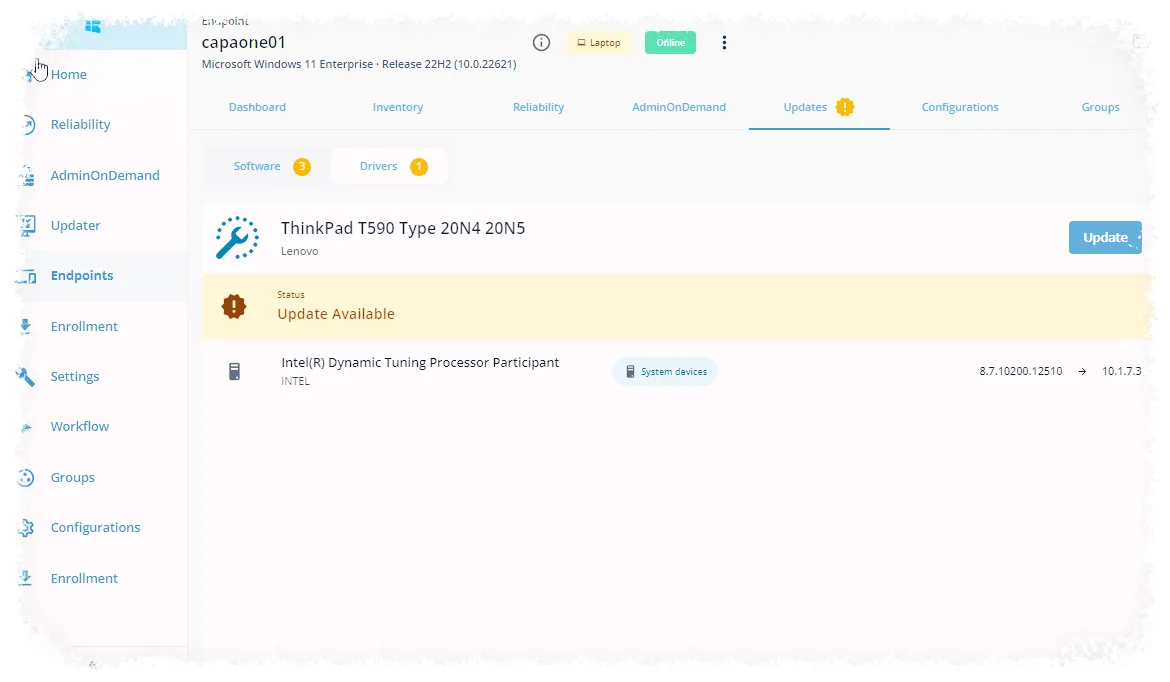
CapaOne Drivers automatically detects and updates outdated drivers across all computers in an organization with a single click — manual single-endpoint updates or automated bulk updates across the entire fleet. Compatible with various deployment tools, cloud-based.